Critical Unbound DNS Vulnerabilities Patched: NLnet Labs Releases Version 1.26.1 to Fix Heap Overflow and Remote Code Execution Flaws

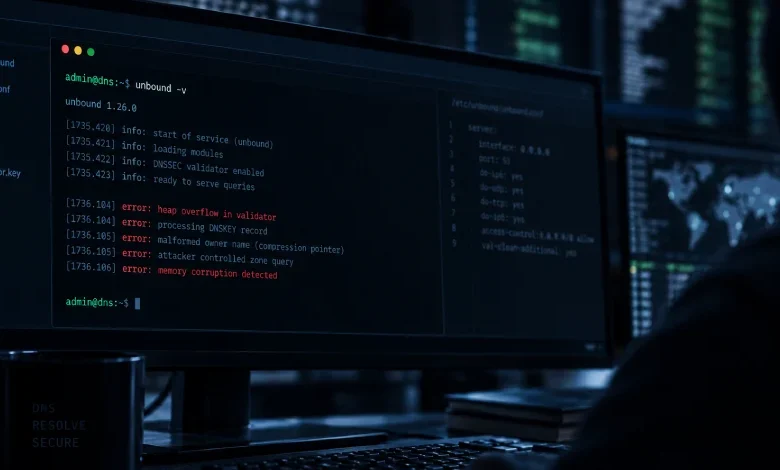
NLnet Labs has officially issued a high-priority security advisory alerting system administrators and network operators worldwide to a critical heap overflow vulnerability residing within the Unbound DNS resolver. Affecting every software release prior to version 1.26.1, the newly disclosed security flaw—officially cataloged and tracked as CVE-2026-81642—resides directly inside the application’s DNSSEC validator component. If successfully weaponized by a malicious actor controlling an authoritative name server, the bug opens a pathway for remote code execution (RCE) and widespread denial-of-service (DoS) disruptions across vulnerable enterprise networks, recursive DNS infrastructures, and telecommunications backbones.
The software maintainers acted swiftly to neutralize the threat, rolling out Unbound version 1.26.1 alongside dedicated patches designed to address a total of nine distinct vulnerabilities. Among this batch of fixes is another severe heap corruption flaw, designated as CVE-2026-82717, which targets CNAME synthesis mechanisms and was independently discovered and reported by Ben Morris of Anthropic. While neither vulnerability has been actively exploited in the wild at the time of publication—with the Cybersecurity and Infrastructure Security Agency (CISA) tracking exploitation levels as none—cybersecurity analysts and infrastructure engineers are strongly urged to apply the latest updates immediately to avert potential zero-day exploitation campaigns.
An In-Depth Technical Breakdown of CVE-2026-81642
To comprehend the severity of the primary flaw, security professionals must examine how Unbound processes cryptographic DNSSEC records. The critical heap overflow specifically occurs during the validation phase when the resolver digests a maliciously crafted DNSKEY record. In this scenario, the owner name of the DNSKEY record is engineered to act as a compression pointer pointing directly into the record’s own internal data.
When the vulnerable Unbound parser attempts to resolve and unpack this improperly formatted pointer, a memory corruption event is triggered on the heap. Because the memory allocation boundaries are bypassed or improperly managed during the digestion process, an attacker capable of steering query traffic toward a target resolver can manipulate the memory layout. NLnet Labs has confirmed that while the baseline impact primarily involves denial of service via application crashes, sophisticated attackers leveraging attacker-controlled data can elevate the flaw to achieve remote code execution under specific system configurations and compiler optimizations.
The maintainers have assigned a critical severity rating to the DNSKEY vulnerability. Although the National Vulnerability Database (NVD) categorized the identifier as "Awaiting Analysis" shortly after disclosure, NLnet Labs assigned a CVSS score framework placing the threat at a high severity tier due to its network attack vector, which requires zero administrative privileges and no user interaction whatsoever.

The Comprehensive Patch Batch: Nine Vulnerabilities Addressed
Unbound version 1.26.1 is not merely a single-issue patch; it represents a comprehensive security sweep that addresses a total of nine vulnerabilities affecting various components of the resolver stack. Every software version up to and including the legacy 1.26.0 release—including the July security update 1.25.1 and the August release 1.25.2—remains susceptible to multiple items within this newly patched cohort. It is important to note that this new critical vulnerability is entirely distinct from CVE-2026-33278, an earlier critical validator bug patched by NLnet Labs in May.
Below is the complete overview of the vulnerabilities addressed in the 1.26.1 release wave:
- CVE-2026-81642 (Critical): A heap overflow in the DNSSEC validator affecting versions up to and including 1.26.0. Triggered by a malicious zone query, leading to potential remote code execution.
- CVE-2026-82717 (High): A heap corruption flaw involving CNAME synthesis during upstream responses, reported by Ben Morris of Anthropic, affecting versions up to 1.26.0.
- CVE-2026-81634 (High): Triggered by a 255-length query name paired with a massive TCP response originating from a malicious name server, resulting in a denial-of-service condition.
- CVE-2026-77955 (Medium): Affects versions 1.13.2 through 1.26.0 in zones utilizing "zonemd-check: yes" located below a trust anchor, creating a temporal window where tampered zone data can be served.
- CVE-2026-78227 (Medium): Impacts builds configured with
--with-libngtcp2and an activequic-portparameter across versions 1.22.0 to 1.26.0. - CVE-2026-80225 (Medium): Triggered by a sustained, high-volume stream of distinct uncached names funneled over a single TCP or DNS-over-TLS (DoT) connection, leading to service degradation.
- CVE-2026-82720 (Medium): Affects versions 1.12.0 to 1.26.0 compiled with
--with-libnghttp2and an activehttps-portconfiguration, categorized by maintainers as having limited impact. - CVE-2026-85501 (Medium): Involves ReTrap algorithmic complexity attacks (including TagTrap, DelegationTrap, NsecTrap, and AdditionalTrap) served via malicious zones, causing service degradation.
- CVE-2026-77860 (Low): Affects the "serve-expired" code path in versions 1.20.0 through 1.26.0, bypassing prior countermeasures implemented against DNSBomb attacks and risking participation in pulsing DoS amplification campaigns.
As part of the ReTrap mitigation strategy, NLnet Labs has also altered a core configuration default: val-clean-additional is now disabled by default. Consequently, Unbound will no longer validate DNSSEC data located within the additional sections of incoming DNS responses unless explicitly re-enabled by system administrators.
Chronology of Discovery and Coordinated Disclosure
The discovery of the primary heap overflow vulnerability is credited to independent security researchers Yuqi Qiu and Xiang Li, operating out of Nankai University’s AOSP Lab. According to official CVE records and timeline disclosures, the researchers formally reported the heap overflow flaw to NLnet Labs on August 11.
Demonstrating rapid incident response capabilities, NLnet Labs engineers successfully developed a functional patch and transmitted it back to the research team for validation by August 12. Following successful verification by the Nankai University researchers on August 13, the maintainers initiated their standard protocol for privately coordinated vulnerability disclosures. Five weeks following the initial report, the comprehensive remediation package was integrated into the official Unbound 1.26.1 codebase and released to the public on Wednesday, September 17.

Broader Industry Implications and Recommendations for System Administrators
The discovery of multiple memory corruption and algorithmic complexity vulnerabilities within a foundational open-source DNS resolver underscores the persistent security risks inherent in complex parsing engines. Recursive DNS resolvers sit at the absolute perimeter of enterprise and institutional networks, making them prime targets for advanced threat actors seeking to establish lateral movement vectors or disrupt critical digital infrastructure.
Because the flaw does not require authentication or user interaction, any publicly exposed instance of Unbound running versions 1.26.0 or earlier represents an inviting attack surface. Furthermore, major Linux distributions and enterprise operating system maintainers have begun issuing security advisories. For instance, the Debian Security Tracker noted that while package version 1.26.1-1 has been marked as fixed in unstable distributions, stable development branches such as bookworm, trixie, and forky remain vulnerable until downstream package maintainers push out updated binaries.
System administrators and network engineers managing infrastructure dependent on Unbound must immediately undertake the following mitigation steps:
- Immediate Upgrades: Download and deploy Unbound version 1.26.1 directly from the official NLnet Labs distribution channels. Pre-compiled Windows installers, source tarballs complete with cryptographic PGP signatures, and checksum verification files are currently available.
- Source Code Patching: For environments where a full software upgrade is impractical due to stringent change-management cycles, administrators should apply the standalone patches provided in the official NLnet Labs security advisory, which have been verified for stability on version 1.26.0.
- Configuration Audits: Review existing configuration files to account for default changes—specifically regarding
val-clean-additional—and verify that query rate-limiting, TCP connection limits, and DoT/DoH parameters are tightly controlled to mitigate potential auxiliary denial-of-service vectors like ReTrap. - Monitoring and Telemetry: Closely monitor recursive resolver logs for anomalous query patterns, disproportionate TCP connection retention, or unusual spikes in memory consumption that could indicate active reconnaissance or exploitation attempts against local infrastructure.
As threat actors continually refine their techniques to target foundational network protocols, prompt patch management remains the single most effective defense in safeguarding enterprise perimeter security against sophisticated remote code execution vectors.
Related posts: