The Reality of AI in Cybercrime: Why Artificial Intelligence is Often Making Attacks Less Effective

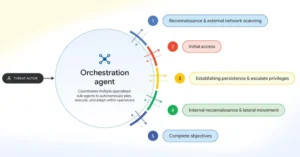
For the past several years, the cybersecurity industry has been dominated by a singular, persistent narrative: the rise of Artificial Intelligence (AI) will inevitably herald an era of “super-powered” cyberattacks. Industry analysts, security vendors, and government officials have frequently cautioned that generative AI and large language models (LLMs) would grant threat actors the ability to scale operations, automate vulnerability research, and craft perfectly tailored social engineering lures. However, as the dust begins to settle on the early integration of these tools into criminal workflows, empirical evidence from the front lines of threat intelligence suggests a significantly different reality.
At the IRISSCON 2026 conference held in Dublin on November 11, Selena Larson, a principal threat researcher at Proofpoint, delivered a provocative assessment that challenges the prevailing industry consensus. According to Larson, the much-vaunted “AI-driven revolution” in cybercrime has failed to materialize as a force multiplier for sophistication. Instead, in numerous observed campaigns, the reliance on generative AI has led to a degradation of attack quality, characterized by technical errors, logical inconsistencies, and an increase in detectable, low-effort output.
The Myth of the AI-Enabled Super-Hacker
Since the widespread public adoption of generative AI tools in early 2023, the cybersecurity community has been inundated with warnings regarding the democratization of hacking. The theory posited that AI would allow even novice threat actors to leverage the same resources as elite state-sponsored groups. The assumption was that AI would function as a force multiplier, enabling faster discovery of zero-day vulnerabilities, the automated writing of exploit code, and the creation of indistinguishable phishing lures.
Larson dismisses these assertions as “marketing nonsense.” Her research, based on the systematic monitoring of threat actor behavior over the last 18 months, indicates that the data simply does not support the premise that AI automatically elevates the skill level of a malicious actor. While AI has undoubtedly increased the speed and volume of attack attempts, it has simultaneously introduced a level of “AI slop”—a phenomenon where reliance on automated generation leads to a breakdown in execution quality.
The Rise of AI Slop and Operational Degradation
The term “AI slop” refers to the accumulation of low-quality, automated content that fails to meet basic standards of functionality or cohesion. Proofpoint’s research has documented this trend across multiple attack vectors, most notably in malware development and phishing campaigns.
In the realm of malware, researchers have identified numerous instances where code generated by AI is functionally inert. Often, the comments within the code suggest an intent that is entirely disconnected from the underlying logic, or the malware fails to execute its payload due to structural errors. This suggests that while AI can draft code, it currently lacks the nuance required to maintain complex, multi-stage infection chains without human oversight—a skill set that many threat actors currently lack.
The degradation is perhaps most visible in Business Email Compromise (BEC) and phishing campaigns. A clear case study is the threat actor tracked by Proofpoint as TA4903. Historically, TA4903 was known for executing sophisticated, well-researched lures that impersonated US government entities to target various industry sectors. However, since the group began integrating AI into their workflows, their effectiveness has plummeted.
The AI-generated lures often feature glaring discrepancies, such as mismatches between the email body, the subject line, and the attached files. In some instances, the AI output has resulted in blank email bodies, rendering the phishing attempt immediately suspicious to both users and automated security filters. Furthermore, the group’s reliance on AI to build phishing websites—a practice sometimes referred to as “vibe coding”—has resulted in simplistic, generic templates that are visually repetitive and easily flagged by modern threat detection systems.
Linguistic Over-Optimization as a Liability
One of the most persistent assumptions regarding AI in cybercrime is that it would solve the “language barrier” for non-native-speaking attackers. Historically, phishing campaigns from certain regions were identifiable by poor grammar, awkward phrasing, and incorrect regional idioms.
Paradoxically, Larson argues that this over-correction has become a liability. Human communication, particularly in business contexts, is rarely perfectly polished. It is often characterized by the idiosyncratic errors, informal grammar, and lack of excessive formality that humans naturally exhibit. When AI generates perfectly grammatically correct, highly formal phishing messages, it often triggers a cognitive dissonance in the recipient. The “too perfect” nature of the message serves as a beacon, alerting the target that the communication is artificial. By removing the human element of imperfection, threat actors are inadvertently making their lures appear less authentic.
Exploitation of Vulnerabilities: Noise Over Precision
The limitations of AI extend into the highly technical domain of vulnerability exploitation. While LLMs are capable of scanning code for potential flaws, the transition from discovery to functional exploitation is where the process frequently fails.
The “BlueMoon” exploit chain, observed in August 2026, serves as a primary example. In this campaign, threat actors attempted to leverage LLMs to write exploits for three chained vulnerabilities in the Microsoft Chrome browser, basing their efforts on information extracted from patch release notes. The resulting exploit code was characterized by significant instability and excessive operational noise.
Instead of a surgical, stealthy intrusion, the AI-generated exploits behaved in ways that were highly visible to security telemetry. The lack of precision and the chaotic nature of the code allowed defenders to identify and mitigate the threat with relative ease. This suggests that while AI can process information at scale, it currently struggles to handle the specific, context-dependent requirements of effective exploit development.
Historical Context and Defensive Strategy
The timeline of AI integration in cybercrime has been rapid but shallow. Throughout 2024 and 2025, the focus remained on proof-of-concept testing. By 2026, the industry moved into a phase of widespread, albeit unrefined, adoption. Throughout this period, the fundamental pillars of cybersecurity—defense-in-depth, robust identity management, and employee training—have remained the most effective deterrents.
From the perspective of a defender, the rise of AI-generated attacks does not necessitate a shift in priority. The core challenge remains the same: preventing unauthorized access and detecting anomalous behavior. While AI may allow attackers to launch more campaigns, the efficacy of those campaigns is still tethered to the competency of the human operator.
As Larson noted, “AI is only as good as its operator.” This principle holds true regardless of the tool being used. If an attacker is fundamentally unskilled, providing them with advanced AI tools will not turn them into an advanced persistent threat (APT). It will merely allow them to fail faster and more frequently.
The Future of the Threat Landscape
The implications of these findings are profound for the cybersecurity industry. Organizations are often pressured into investing heavily in AI-driven defensive tools, under the impression that they are engaged in an “AI vs. AI” arms race. However, if the adversary’s AI-driven attacks are fundamentally flawed and easily detectable, the necessity for a reactionary, AI-heavy defensive posture may be overstated.
Instead, the evidence supports a return to basics. The focus should remain on hardening systems against the same categories of vulnerabilities that have existed for decades. Because AI is currently acting as a catalyst for the rapid exploitation of known vulnerabilities, the importance of patch management and configuration hygiene has never been higher.
The threat landscape is indeed evolving, but perhaps not in the manner suggested by sensationalist headlines. The shift is not toward a future of autonomous, sentient AI hackers, but toward a crowded environment filled with noisy, automated, and ultimately fragile attack attempts. For the security professional, the objective remains clear: continue to focus on the fundamental defensive measures that have historically provided the best protection against both human and automated threats. AI, for all its potential, has yet to demonstrate that it can replace the strategic thinking and tactical precision of a human threat actor—and until it does, the traditional defensive playbook remains the most robust defense.
Related posts: