BragJack Vulnerability Exposes Critical Security Flaws in AI-Powered Browser Assistants

Security researcher Gal Weizman of Forever Security has disclosed a sophisticated attack vector known as BragJack, which allows malicious browser extensions to hijack AI assistants integrated directly into modern web browsers. This vulnerability, which affects major platforms including Google Chrome, Microsoft Edge, Opera, and Perplexity, demonstrates how the increasing integration of "agentic" AI—models capable of performing tasks on a user’s behalf—introduces significant new attack surfaces for endpoint security.
The proof-of-concept research successfully compromised five distinct AI-enabled browsing environments: Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and the Claude for Chrome extension. The discovery resulted in over $20,000 in bug bounty rewards across multiple vendors, with individual payouts ranging from $600 to $7,000. Furthermore, the findings led to the assignment of at least two formal Common Vulnerabilities and Exposures (CVE) identifiers, specifically CVE-2026-0628 and CVE-2026-55945, highlighting the severity of the architectural oversight.
The Mechanics of the Attack: Brains and Bodies
At the core of the BragJack methodology is a fundamental shift in how browsers operate. Weizman categorizes modern AI-integrated browsers into two distinct components: a "brain," which interprets user intent and processes complex instructions, and a "body," which represents the browser’s privileged internal systems responsible for executing actions—such as manipulating tabs, accessing local files, or capturing screenshots.
Traditionally, browser extensions are confined by sandboxing and permission models designed to prevent unauthorized access to sensitive system resources. However, BragJack exploits the trust relationship between the browser’s web-based AI interface and the privileged internal APIs that the AI uses to interact with the system.
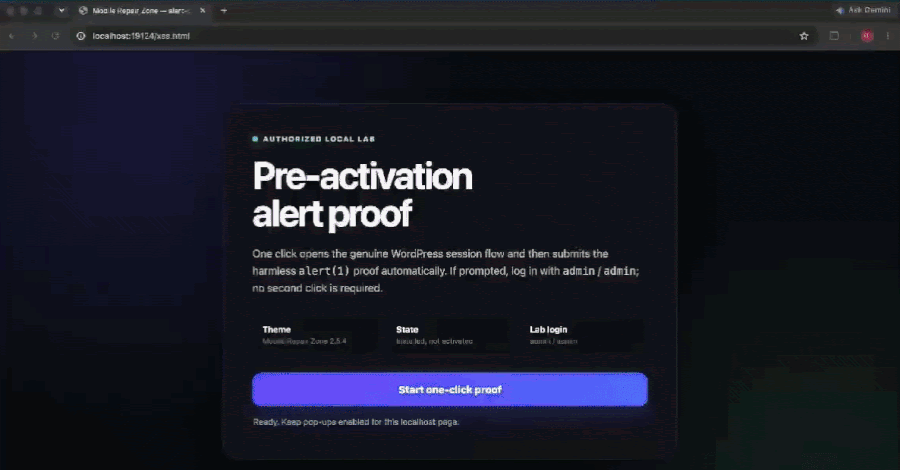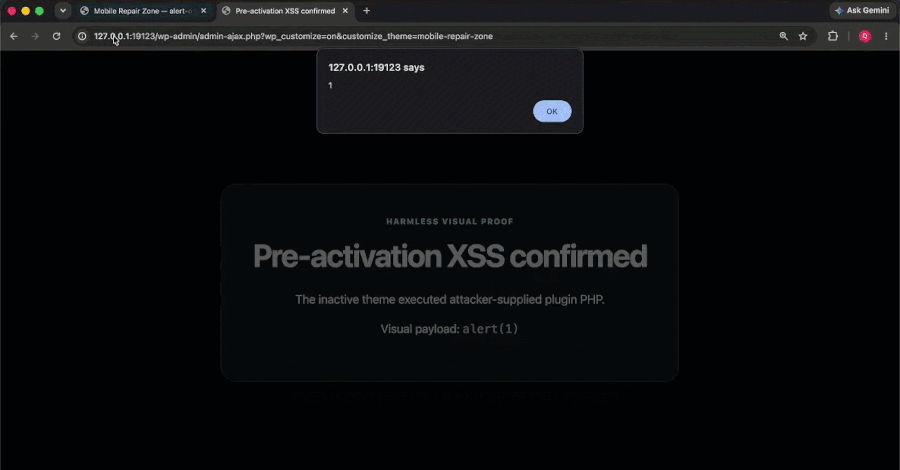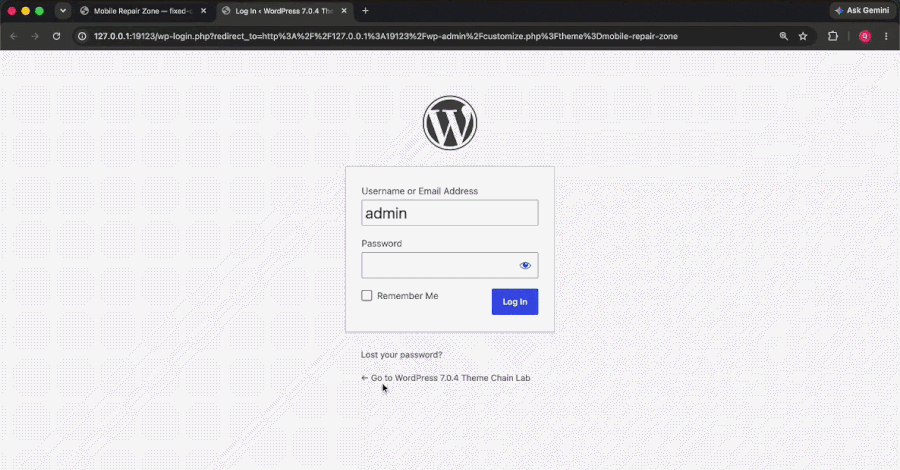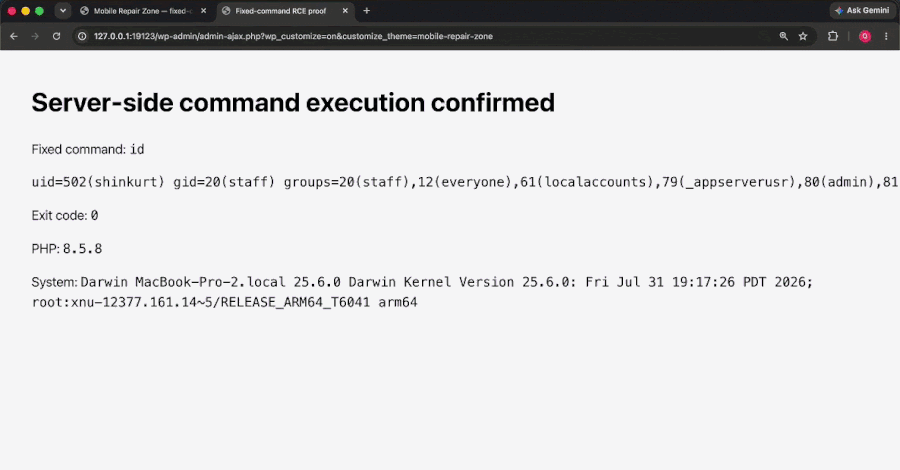
The attack utilizes Chromium’s declarativeNetRequest (DNR) functionality. DNR is an API that allows extensions to modify network traffic, including the ability to redirect resources and alter HTTP headers. By weaponizing this legitimate developer tool, an attacker can manipulate the requests made by an embedded AI web application. In the case of Google Chrome, Weizman demonstrated that even when an extension is restricted from directly injecting scripts into privileged internal pages (such as chrome://glic), the DNR rules can intercept the underlying web app requests. By weakening security headers and forcing a malicious redirect of JavaScript resources, the attacker can effectively "masquerade" as a trusted process, allowing the extension to communicate directly with the browser’s AI component.
Chronology of Discovery and Mitigation
The discovery process took place over several months, with findings reported to various vendors throughout 2026.
- Early 2026: Initial research by various security entities, including Manifold Security, identified weaknesses in the Claude for Chrome extension, noting that it processed synthetic clicks without user verification.
- April 2026: LayerX disclosed the "ClaudeBleed" vulnerability, which highlighted that the extension trusted the origin of
claude.aiwithout validating which specific script was driving the interaction. - Q3 2026: Gal Weizman formalized the BragJack research, identifying that the issue was not isolated to a single extension but was a systemic flaw in how AI-agentic browsers handle trust.
- September 2026: Official disclosure of the BragJack findings. Google and Microsoft confirmed the resolution of the specific CVEs assigned to their platforms shortly thereafter.
The response from the tech industry has been rapid, with major browser vendors patching the identified race conditions and permission bypasses. However, the recurring nature of these vulnerabilities—evidenced by the Claude extension remaining susceptible for eight consecutive releases—suggests that securing AI-integrated software requires a departure from standard web security models.
From Information Theft to Agentic Control
While simple browser exploits often focus on data exfiltration, the BragJack attack is uniquely dangerous because it targets "agentic" capabilities. In environments like Perplexity Comet or Opera Neon, the AI is not merely a chatbot; it is designed to act on the web.

In the case of Perplexity Comet, the browser’s internal agent trusted specific Perplexity domains for testing purposes. These testing environments often lack the stringent security controls enforced on production sites. By using DNR rules to bypass redirects and load these less-secure domains, an attacker can inject content scripts that gain full control over the AI agent.
Once this control is established, the agent can be weaponized to perform tasks that the user never authorized. During his demonstration, Weizman successfully forced an AI agent to browse through a user’s private emails, summarize the contents, and transmit that data to an external, attacker-controlled server. Because the AI is acting within its "legitimate" role, these actions often bypass traditional endpoint protection platforms (EPP) and data loss prevention (DLP) tools, which are not designed to flag a "helpful" AI assistant as a threat.
The Challenge of "Prompt Forcing"
Weizman introduces the term "Prompt Forcing" to describe the technique of hijacking the AI’s instruction set. Unlike classic prompt injection, which involves tricking an AI into ignoring its safety guidelines through clever phrasing, Prompt Forcing involves handing the AI agent an entire, pre-validated instruction chain.
Because the AI is designed to be a "helpful assistant," it treats the forced prompt as a valid command from the user. When the AI then translates these instructions into browser actions, it does so using its elevated privileges. The security implication is profound: the malicious activity is performed by the browser’s own trusted, signed code. From the perspective of system logs, the action appears as a standard, authorized operation performed by the browser’s AI engine.
Implications for Future Security Architectures
The BragJack disclosure serves as a sobering reminder that the rapid deployment of generative AI into consumer software is often outpacing the security frameworks designed to protect them. As browsers evolve from simple document viewers into complex operating environments for AI agents, the boundary between the "user" and the "AI assistant" is blurring.
Security analysts suggest that vendors must move toward a "Zero Trust" model for AI agents. This would involve:
- Strict Isolation: Ensuring that browser-level AI agents cannot access sensitive system resources without explicit, user-verified intent for every individual action.
- Contextual Validation: Requiring that AI agents verify the origin of instructions, ensuring they cannot be triggered by third-party browser extensions or unverified network traffic.
- DNR Auditing: Implementing stricter controls over the
declarativeNetRequestAPI to prevent extensions from redirecting or modifying traffic associated with critical browser components.
For the end user, the risks underscore the importance of browser hygiene. While developers work to harden these systems, the primary defense remains the limitation of browser extensions. Users are advised to audit their installed extensions regularly and remove any that are not strictly necessary, particularly those granted broad "read and change all data" permissions.
As the industry moves toward a future where AI agents manage our personal and professional workflows, the BragJack vulnerability highlights that the most significant threats will likely come not from external malware, but from the subversion of the very tools intended to make our digital lives more efficient. The transition to agentic AI requires not just better models, but a fundamental redesign of the browsers that house them.