Cursor AI Security Breach Exposes Thousands of Developers to Malicious Extensions and Credential Theft

The artificial intelligence-powered code editor Cursor has confirmed a significant security incident involving a multi-stage cyberattack that resulted in the distribution of malicious software via its marketplace and the compromise of sensitive user data. The breach, which originated from a third-party service provider, allowed unauthorized actors to infiltrate Cursor’s internal systems, harvest unredacted credentials from historical AI coding-agent traces, and temporarily host a compromised version of Anthropic’s Claude Code extension. This event serves as a stark reminder of the escalating security risks facing the AI development ecosystem, a phenomenon that cybersecurity researchers have collectively termed "Black October."
The Anatomy of the Breach: From Fireworks AI to the Marketplace
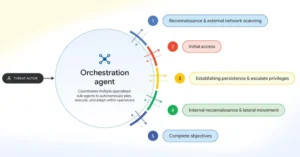
The security compromise began not at Cursor’s own headquarters, but within the infrastructure of Fireworks AI, an external partner utilized by Cursor for AI model training and inference services. According to an incident report published by Cursor, attackers successfully obtained an access key belonging to Fireworks AI. This initial foothold provided the threat actors with the capability to access a read-only storage bucket that Cursor used to facilitate data sharing with the provider.
The storage bucket contained historical AI coding-agent traces, primarily generated during the 2025 calendar year. These traces were collected from users who had not activated "Privacy Mode" within the Cursor environment, a setting that allows data to be used for model training and improvement. Crucially, some of these traces included unredacted API credentials. By leveraging these stolen keys, the attackers moved laterally into Cursor’s internal systems, gaining unauthorized access to various software-as-a-service (SaaS) tools.
The escalation of the attack reached its peak on October 29, when the perpetrators utilized a stolen credential—acquired during the internal system infiltration—to bypass security protocols and inject malicious, unauthorized copies of the Claude Code extension into the cache utilized by the Cursor VS Code extension marketplace.
Chronology of the Incident
The timeline of the attack highlights the speed at which modern supply chain compromises can unfold:
- Pre-October 29: Attackers gain access to a Fireworks AI access key, allowing them to scrape historical AI traces from a read-only storage bucket.
- October 29 (Morning): Using credentials harvested from the traces, attackers compromise internal Cursor systems. They publish malicious versions of the Claude Code extension (specifically versions 2.1.312 and 2.1.313) to the Cursor marketplace cache.
- October 29 (11-Hour Window): The malicious extensions are served to unsuspecting users. During this time, up to 5,000 developers are estimated to have downloaded the compromised builds.
- Post-Discovery: Cursor’s internal monitoring systems flag the unauthorized activity. The company immediately revokes the compromised Fireworks access key and begins a systematic rotation of all exposed credentials.
- Immediate Response: Cursor takes the precautionary measure of temporarily disabling several internal services and product features to contain the breach.
- November (Ongoing): The company conducts a thorough audit, moves all inference traffic away from the affected Fireworks infrastructure, and redeploys its production environment to ensure no residual backdoors remain.
Impact on the Developer Community
The primary objective of the malicious extension was to establish persistence on developer workstations. Once installed, the modified Claude Code extension executed a malicious JavaScript payload designed to compromise the host environment. The malware was engineered to scan for system information and attempt the installation of an attacker-controlled SSH key. By configuring these persistence mechanisms, the attackers sought to gain long-term, unauthorized remote access to the machines of Cursor users.
Despite the sophisticated nature of the payload, security analysts observed that the malware contained coding errors that likely hindered its effectiveness on many Windows and macOS environments. Specifically, the backdoors struggled to activate on machines where SSH was not pre-configured or enabled. Nevertheless, the potential exposure of 5,000 developers represents a significant supply chain risk. Cursor has confirmed that while the extension marketplace was compromised, the official Anthropic repository and the Open VSX marketplace remained unaffected throughout the ordeal.
Regarding the scope of the data exposure, Cursor has maintained a high degree of transparency. The company reports that fewer than 0.05% of its total user base had their coding-agent traces accessed, and even fewer—less than 0.01%—had actual API credentials exposed. Official application releases, customer code repositories, and the data of users who had enabled Privacy Mode were reportedly shielded from the breach.
The "Black October" Context: A Broader Trend
The incident at Cursor is not an isolated event but rather part of a concentrated wave of attacks targeting the AI development infrastructure sector. The security firm Wiz, which has been tracking these developments, has labeled this period "Black October." The common thread among these incidents is the targeting of the foundational layers of AI development, specifically the authentication mechanisms that guard access to powerful AI models and development tools.
The implications of these attacks are multi-faceted. In several cases documented by researchers, stolen credentials were used to perform unauthorized AI inference, leading to exorbitant, fraudulent charges for the companies involved. In others, attackers attempted "model distillation"—a process of extracting the knowledge of a proprietary, high-performance AI model into a smaller, cheaper, and often unauthorized alternative.
Other notable victims of this trend include:
- Railway: An incident involving the theft of customer authentication secrets resulted in approximately $740,000 in fraudulent AI-related service charges.
- OpenCode: This platform disclosed a breach involving exposed API keys, which were subsequently exploited for unauthorized AI usage.
- Warp: The company reported a security event that exposed AI agent logs and user telemetry data.
- Notion: A breach at Fireworks AI, the same provider involved in the Cursor incident, led to the exposure of AI chat transcripts for a subset of Notion users.
Official Response and Remediation
In the wake of the breach, Cursor has adopted a "zero-trust" approach to its infrastructure recovery. The company’s engineering teams have rebuilt the extension marketplace from the ground up and performed a full redeployment of their production infrastructure. By severing ties with the specific Fireworks AI infrastructure that allowed the initial breach, Cursor aims to isolate its operations from further third-party vulnerabilities.
"We have taken immediate action to rotate all credentials that may have been touched during this incident," Cursor stated in their public security notice. "We are working closely with cybersecurity experts to audit our systems and ensure that our security posture meets the high standards our users expect."
Affected users have been advised to follow a strict remediation protocol, which includes revoking any API keys that were active during the October 29 window and checking their local machines for the presence of unauthorized SSH keys or suspicious background processes.
Analysis: Implications for the AI Ecosystem
The Cursor breach highlights a critical vulnerability in the modern software development lifecycle: the reliance on third-party AI infrastructure. As AI-powered tools become deeply integrated into the IDE (Integrated Development Environment), the attack surface for developers grows exponentially.
The incident underscores three vital lessons for the industry:
- The Danger of "Implicit Trust": Developers often grant broad permissions to AI extensions. This breach demonstrates that even reputable extensions, if compromised at the source, can serve as a conduit for severe system-level access.
- Data Sensitivity in Training Logs: The fact that historical traces contained unredacted credentials proves that logging practices in AI development are currently insufficient. Developers and companies must ensure that PII (Personally Identifiable Information) and security secrets are scrubbed before data is sent to training or inference buckets.
- The Supply Chain Bottleneck: Security is only as strong as the weakest link in the supply chain. For Cursor, that link was an external provider. For the broader industry, the reliance on shared, interconnected infrastructure means that one successful hack can have a cascading effect across multiple platforms.
As the industry moves forward, the focus is shifting toward "Privacy-First" AI development. Features like Cursor’s Privacy Mode, which keeps user data siloed and prevents it from being used for training, are becoming a necessity rather than an optional setting. The events of "Black October" have effectively forced a maturation of the AI developer platform market, where security is now being positioned as a core competitive differentiator rather than an afterthought. Moving forward, developers should expect more rigorous vetting of extensions, mandatory multi-factor authentication for all AI service access, and a more cautious approach to the data they share with AI-assisted coding tools.
Related posts: