Binance Hackers Exploited Aave DeFi Lending Protocol to Launder Millions in Stolen Stablecoins

The landscape of cryptocurrency security and decentralized finance (DeFi) experienced a profound stress test following one of the largest digital asset exploits in history. Perpetrators behind the monumental Binance security breach executed a sophisticated laundering operation, leveraging the prominent decentralized lending protocol Aave to convert illicitly obtained stablecoins into native Ethereum. This strategic maneuver was specifically designed to circumvent centralized asset-freezing mechanisms, exposing deep operational vulnerabilities at the intersection of centralized exchanges and permissionless financial infrastructure.
The Mechanics of the Exploit and Laundering Strategy
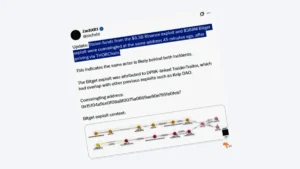
On-chain forensic data revealed the precise architecture of the post-exploit laundering phase. A wallet address directly linked to the attackers deposited approximately $60 million worth of Tether (USDT)—which had been stolen during the unprecedented Binance security breach—as collateral on the Aave V3 protocol operating on the Ethereum network.
Using this substantial capital as backing, the perpetrators borrowed 19,762 wrapped Ether (WETH), valued at roughly $44.6 million at the time of the transaction. This maneuver highlights a critical structural asymmetry in cryptocurrency investigations. Centralized stablecoin issuers, such as Tether and Circle, possess the technical capability to blacklist addresses and freeze tokens associated with illicit activities, effectively neutralizing stolen assets if they remain in their native token format.
However, layer-1 native assets like Ethereum and its wrapped variants operate on immutable, permissionless ledgers without a central authority capable of freezing individual addresses or reversing transactions. By depositing USDT into Aave, the attackers effectively leveraged the stolen stablecoins to acquire an alternative, harder-to-freeze asset without needing to liquidate the stablecoins directly on centralized exchanges where emergency freezes could be enforced. The acquired WETH could subsequently be bridged across networks, routed through privacy-enhancing protocols, or swapped into native ETH, drastically complicating recovery efforts for law enforcement and blockchain analytics firms.

Chronology of Events and the Race Against Time
The execution of the Aave transaction demonstrated a high degree of operational planning, particularly regarding timing. The critical phase of the laundering process unfolded within a narrow three-minute window, taking place between 20:58 and 21:01 UTC.
On-chain analysis indicates that this activity occurred approximately 40 minutes before Aave and its associated risk management partners initiated emergency protocol freezes. This razor-thin margin allowed the hackers to successfully interact with the lending smart contracts and extract liquidity before governance mechanisms could restrict new borrowing activities across the affected markets.
Following the detection of the abnormal activity, Aave protocols confirmed that the malicious position held approximately $59.9 million in USDT collateral backed against $43.8 million in outstanding WETH debt. Crucially, subsequent technical audits and protocol statements confirmed that Aave’s smart contracts were not compromised, nor was there any technical exploit of the lending platform’s code. Instead, the perpetrators utilized the protocol’s intended, legitimate financial functionality as an exit route, demonstrating how open-source decentralized infrastructure can inadvertently serve as a laundering conduit during major exchange hacks.
Emergency Response and Cross-Chain Mitigation
In response to the unfolding crisis, Aave governance and its decentralized risk service providers initiated a coordinated emergency containment strategy. The intervention was sweeping, designed to halt potential cascading risks and prevent further exploitation of lending reserves.
The emergency protocol freeze encompassed:

- 175 distinct liquidity reserves operating on Aave V3 deployed across 16 different blockchain networks.
- 117 liquidity reserves operating on Aave V4 deployed across 4 networks.
Risk management teams temporarily disabled borrowing and new deposits for these specified reserves while maintaining withdrawal functionalities for legitimate users where possible. This rapid mitigation effort prevented the attackers from scaling their positions further or draining additional liquidity from the broader ecosystem. Industry security analysts noted that while the emergency response was exceptionally fast by decentralized governance standards, the incident nonetheless underscores the immense pressure placed on decentralized autonomous organizations (DAOs) and risk providers when confronting sophisticated, well-resourced threat actors.
Broader Implications for Decentralized Finance
The exploitation of Aave’s lending architecture following the Binance breach has ignited intense debate within the global blockchain community regarding the fundamental philosophy of decentralized finance. DeFi protocols are intentionally built upon permissionless architecture—systems designed to operate without gatekeepers, KYC (Know Your Customer) requirements, or centralized censorship.
However, this core tenet creates a profound vulnerability when criminal entities utilize decentralized liquidity pools to launder large-scale corporate or exchange thefts. Because smart contracts execute deterministically based on code rather than intent, a protocol cannot inherently differentiate between a legitimate user depositing collateral and a malicious actor washing stolen exchange funds.
Financial regulators and compliance advocates point to such events as evidence that decentralized protocols must adopt more sophisticated, integrated risk mitigation layers—such as address-screening or preemptive circuit breakers—without entirely compromising their permissionless ethos. Conversely, decentralized proponents argue that introducing centralized filtering or freezing capabilities at the smart contract level undermines the censorship-resistant properties that form the foundational value proposition of public blockchains.
As blockchain forensics firms continue to track the movement of the WETH acquired during the incident, the episode serves as a watershed moment for the industry. It illustrates that as security protocols on centralized platforms strengthen, bad actors are increasingly pivoting toward sophisticated cross-chain maneuvers and DeFi primitives to obscure the provenance of stolen capital, forcing both centralized institutions and decentralized protocols to re-evaluate their security co-dependencies.